
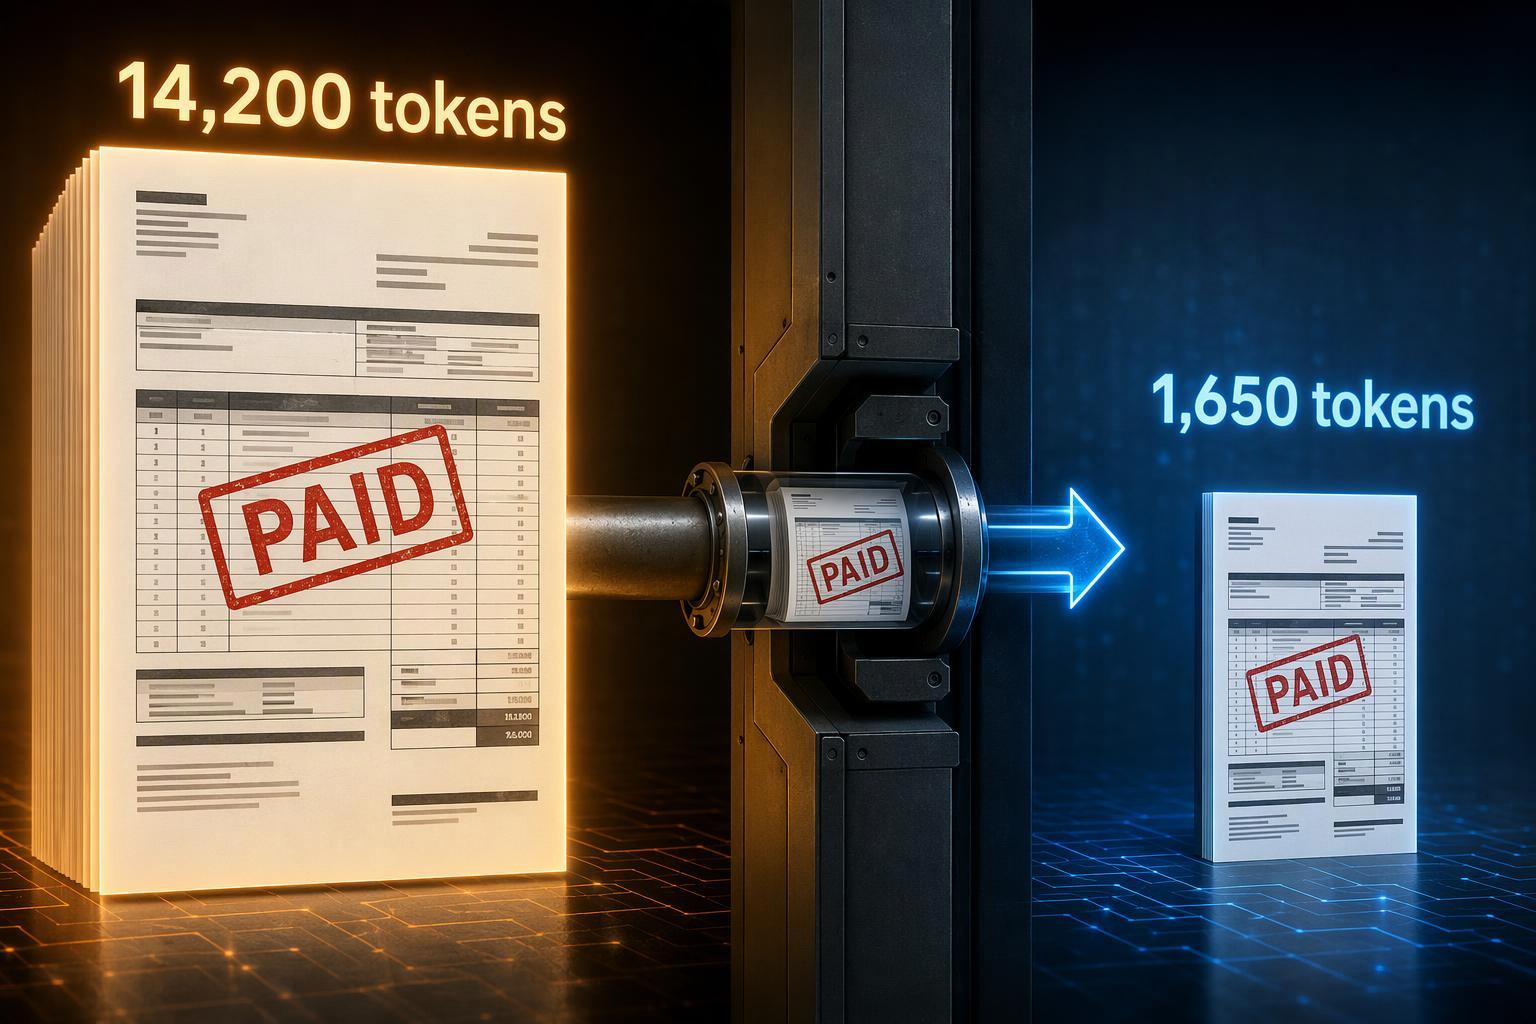
Most of an Agent's Bill Is Paid Before It Reasons
A single team's rebuild cut tokens per LLM call from 14,200 to 1,650 on the same pages. Why ingestion cost, not model price, drives agent bills.
44 min read
In-depth reviews of the latest digital products including smartphones, laptops, audio devices, and more to help you make informed decisions
A single team's rebuild cut tokens per LLM call from 14,200 to 1,650 on the same pages. Why ingestion cost, not model price, drives agent bills.
Agent-run experiments shift reproducibility from human notes to execution traces. Why capture at execution time belongs in every agent-ification project's acceptance criteria.
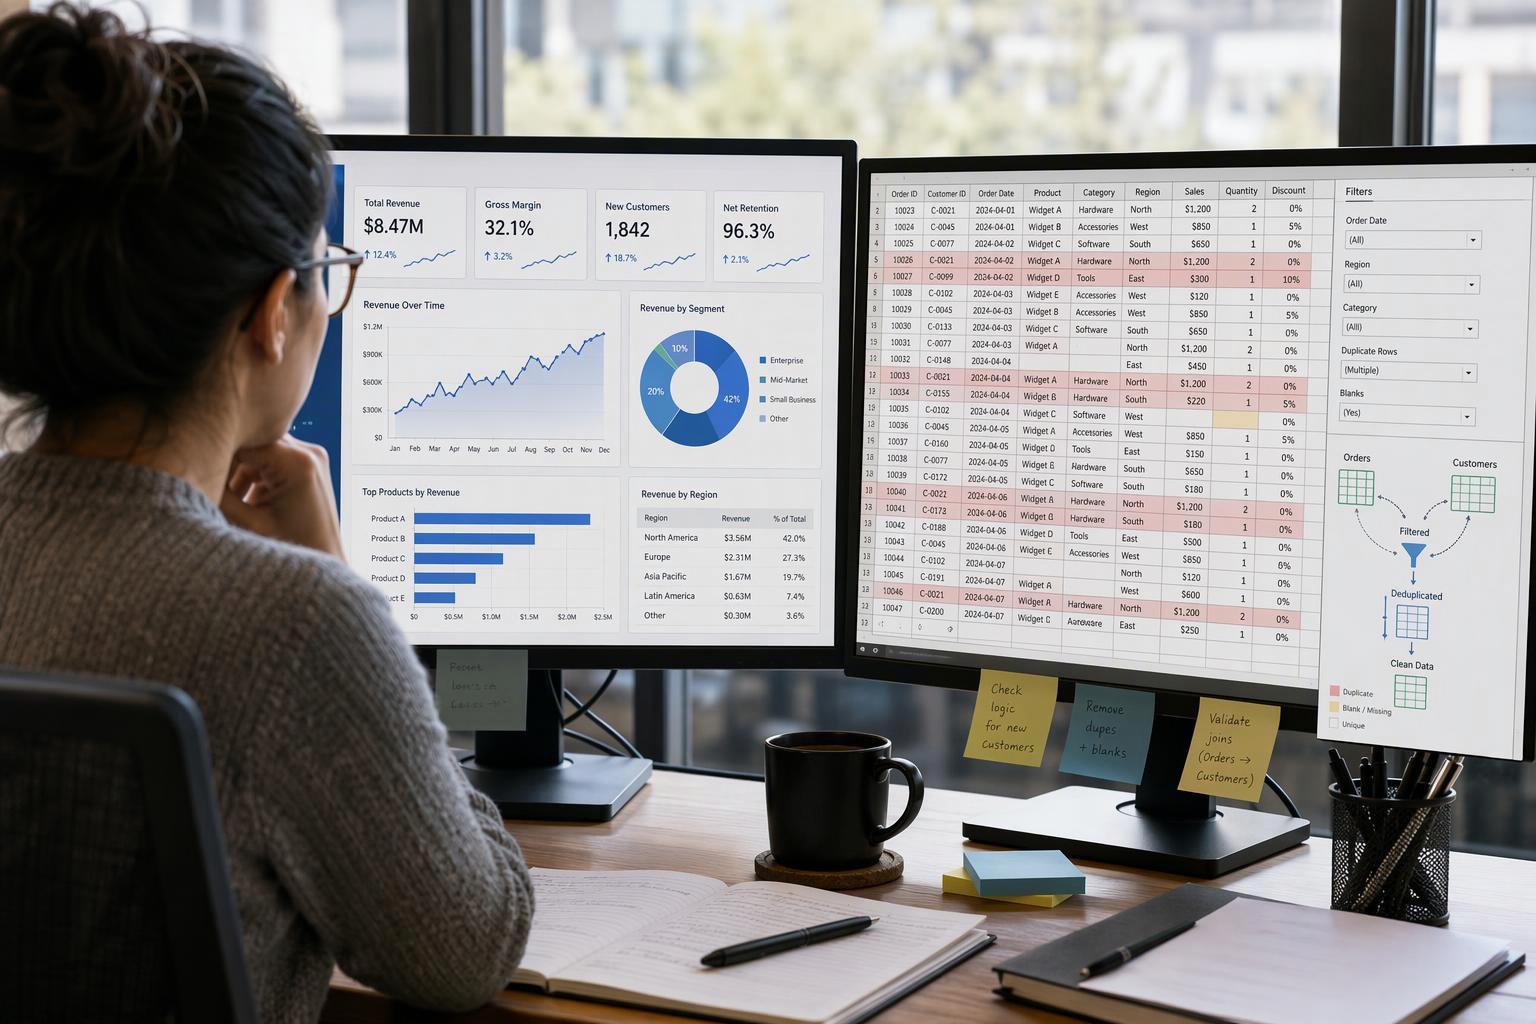
A practical way to count the repeated cleaning, joins and de-duplication hidden behind BI dashboards, and to decide which preparation belongs in a shared, reusable data foundation.
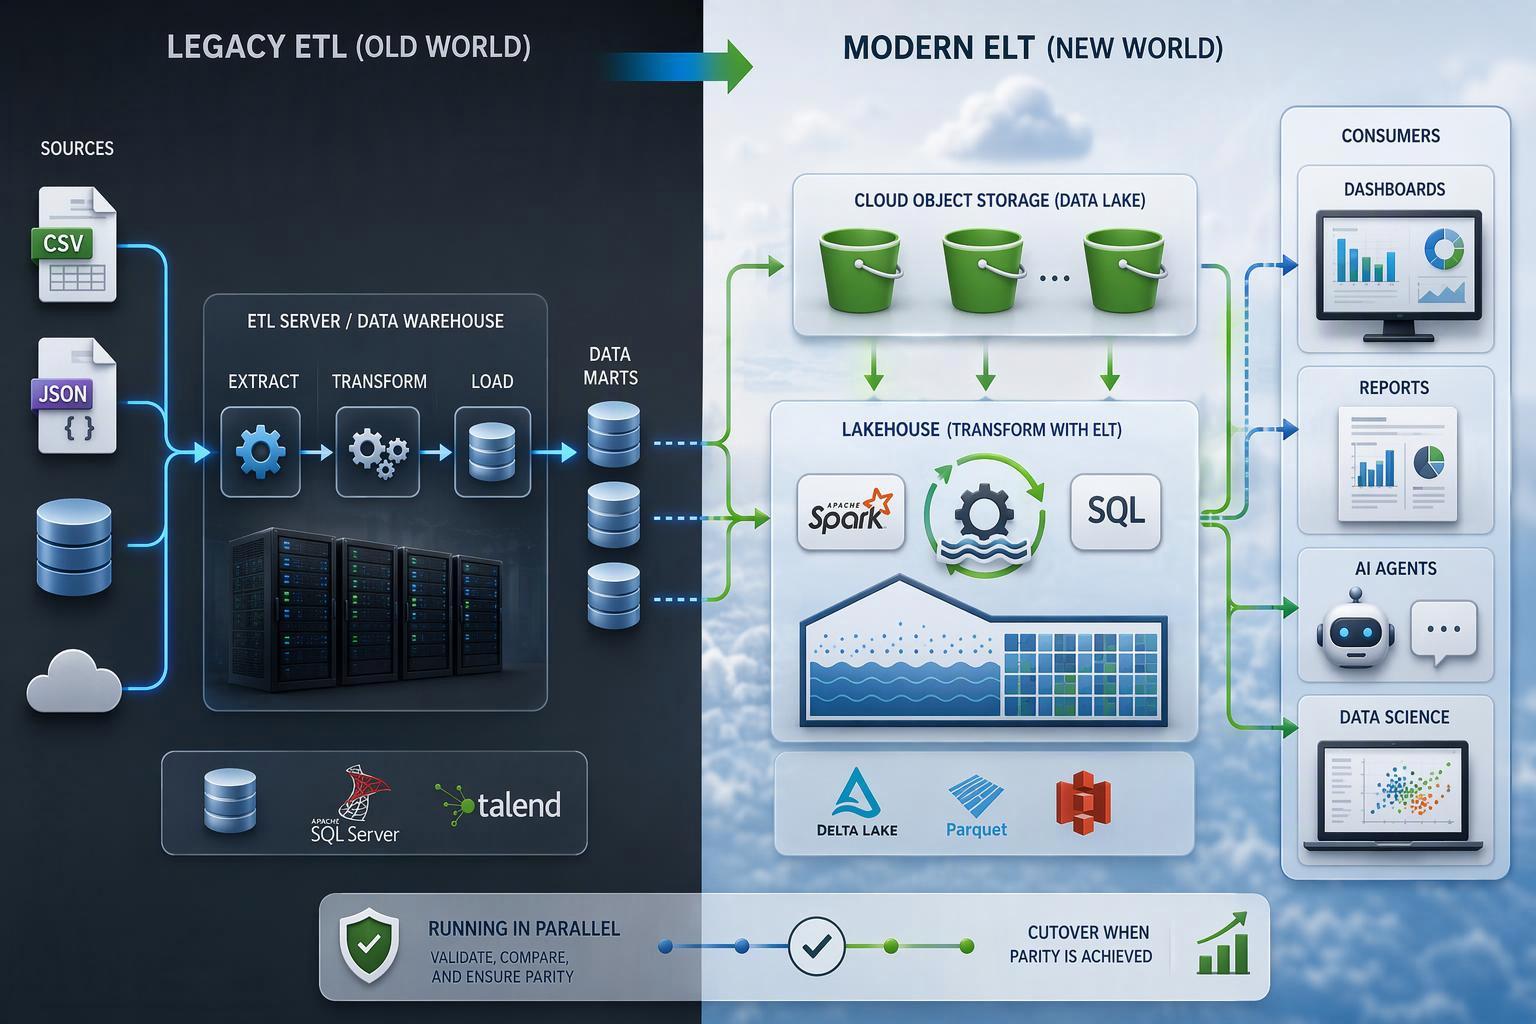
A step-by-step ETL to ELT migration guide: land raw extracts in an object-storage landing zone, move transformation logic into the lakehouse, and run parallel synchronization until parity and near real-time freshness are proven for agentic AI consumers.
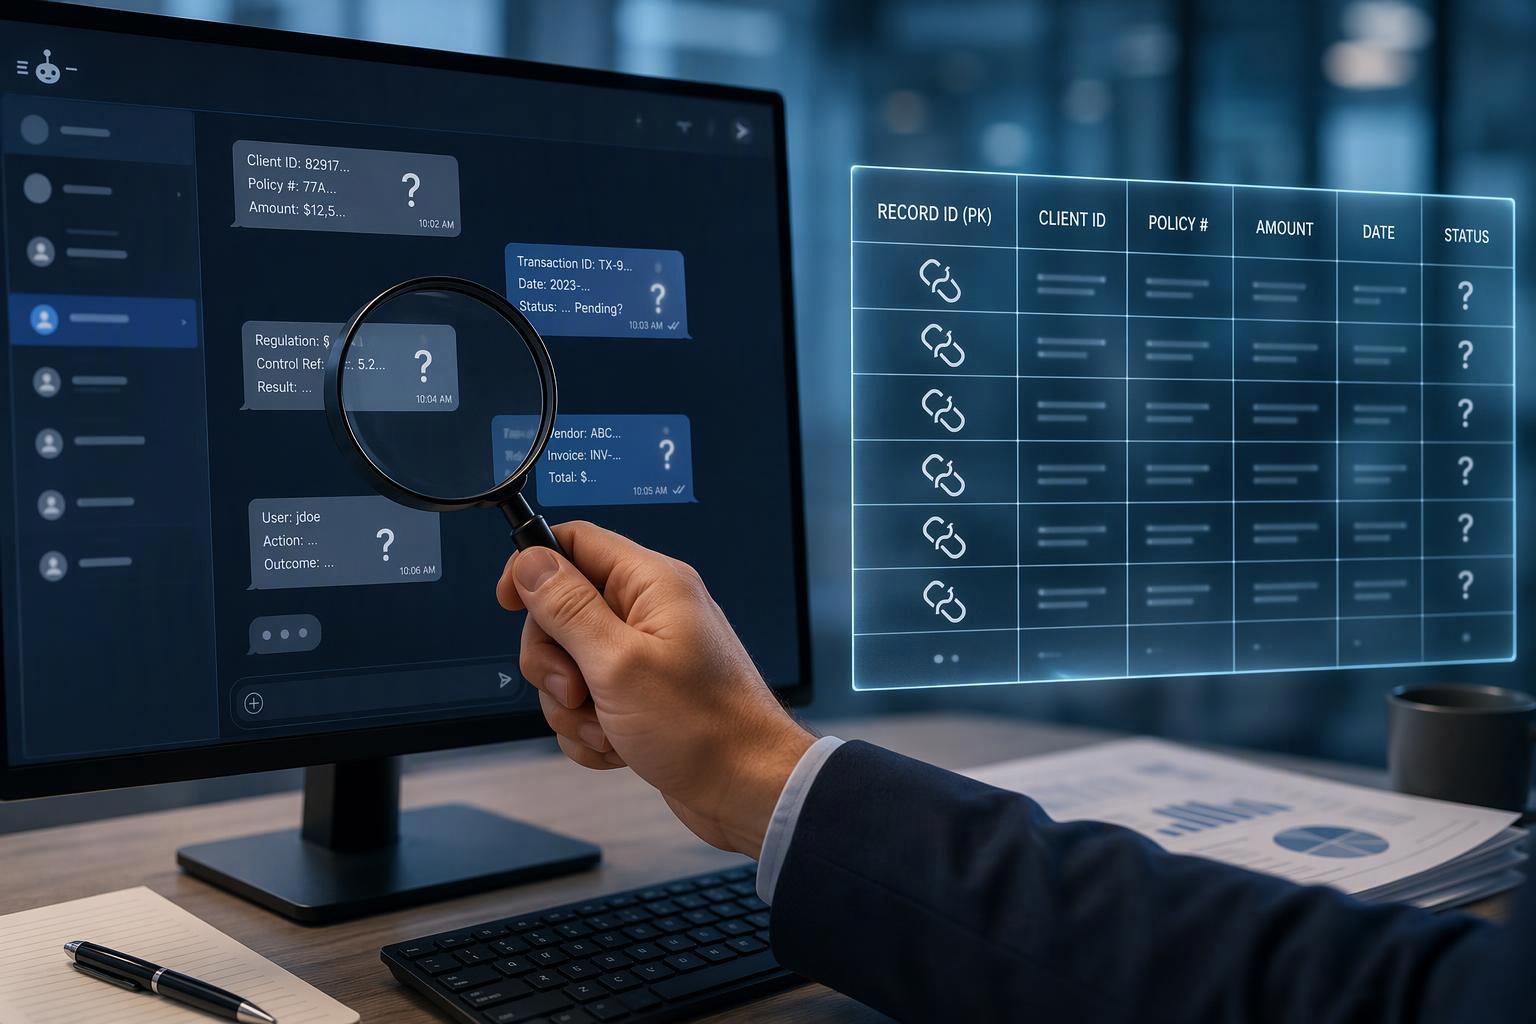
Why a stable record identity contract, not a better model, is the compliance asset: minimum key requirements, five tests that separate record-level controls from narrative summaries, and a vendor-neutral evaluation checklist.
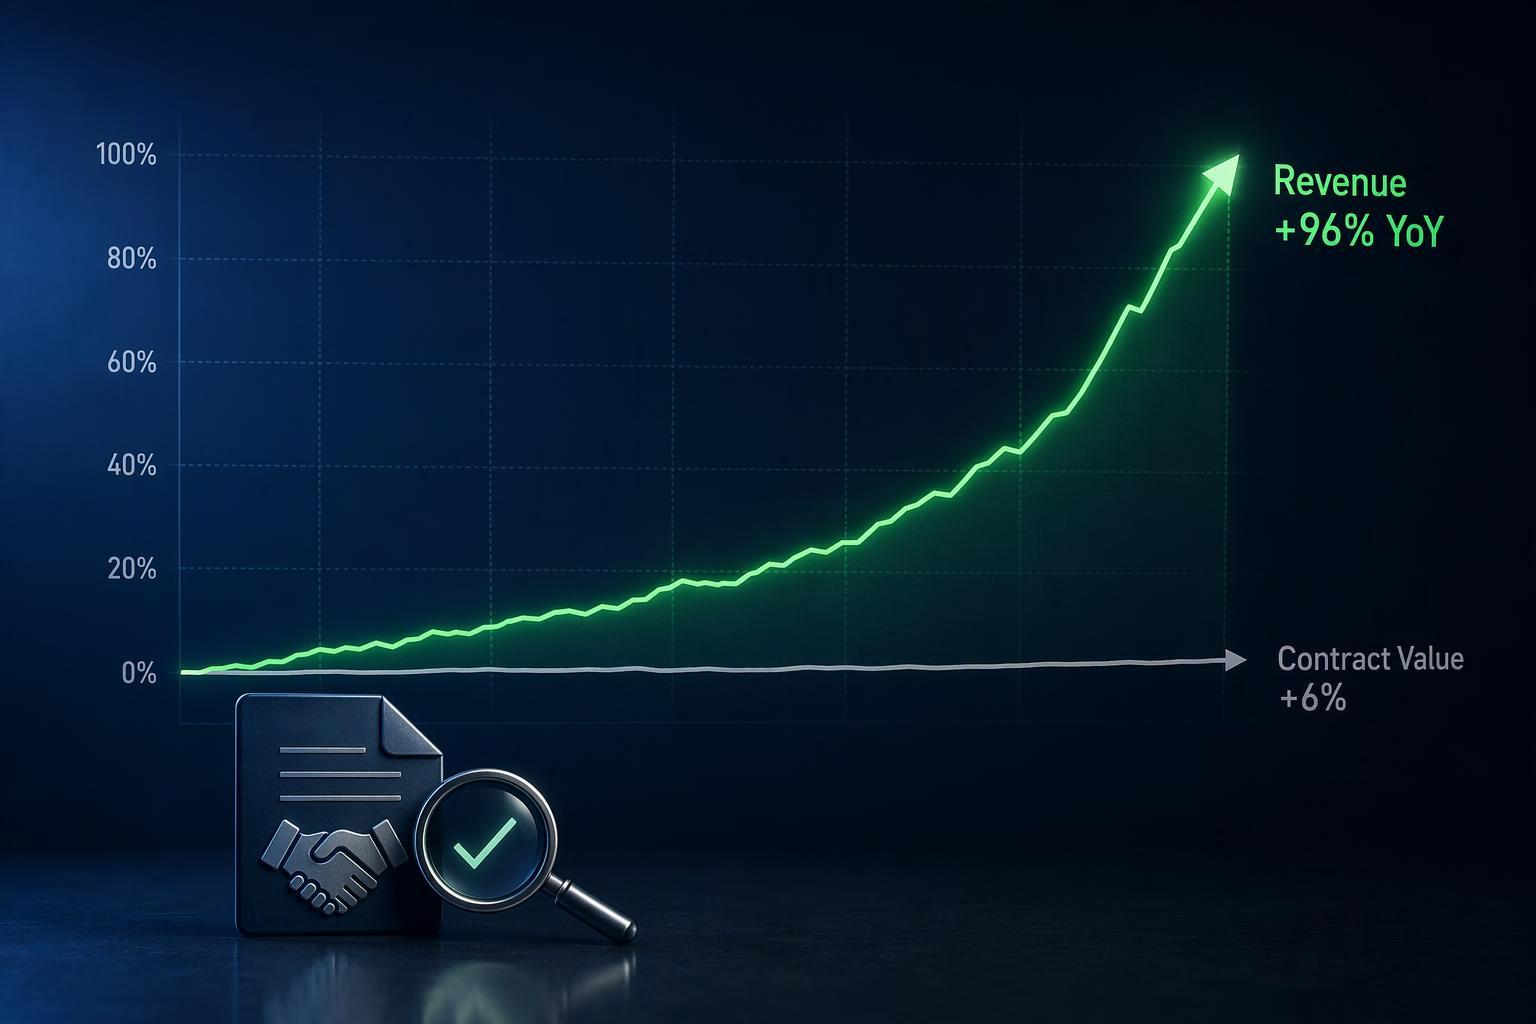
Palantir's Q3 2026 revenue grew 95.9% while total contract value rose 6%. Why AI buyers now fund a chain of bounded, falsifiable proofs instead of multi-year commitments, and the controls that keep those proofs from becoming platform drift.
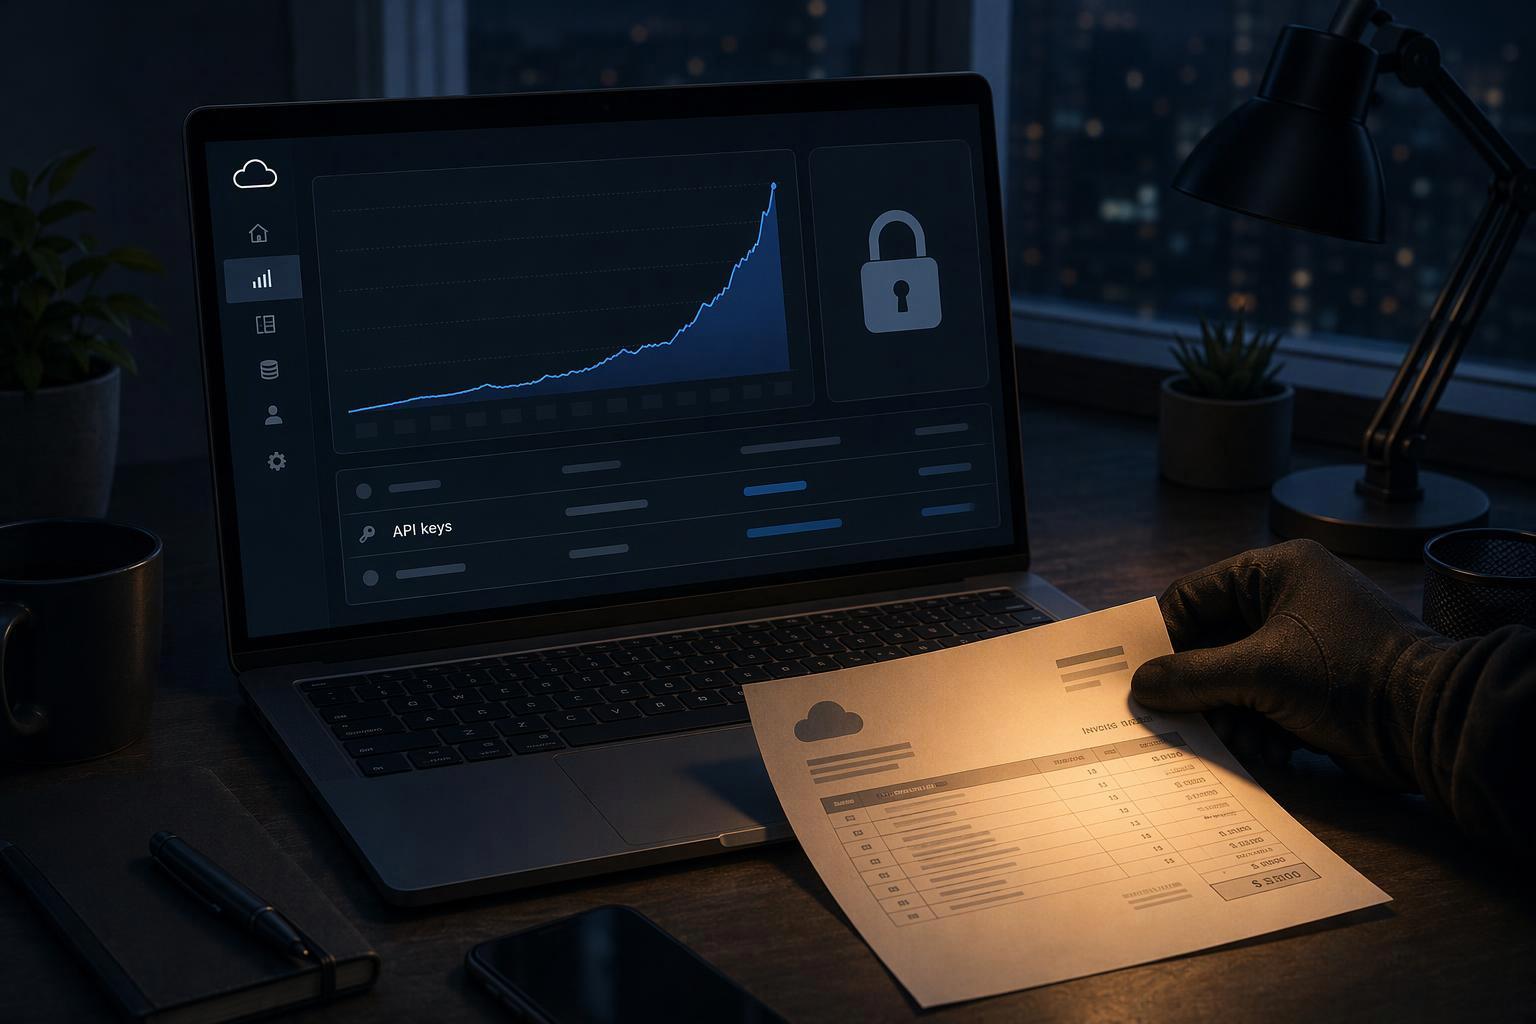
Why stolen API keys on metered AI services are a billing attack, how to separate a theft spike from a workload spike, which controls bound the loss, and a 60-minute response sequence.
Why public corpora are becoming the exception in enterprise AI: dated evidence on robots.txt restrictions, licensing, disclosure duties, plus an acceptance checklist and governance tiers for public, licensed and internal data.
Why a security fix can be downloadable and diffable weeks before its advisory: how to measure the patch-to-advisory window, triage a release with no CVE, and co-release fixes with advisories.